

Instant Download PECB : ISO-IEC-27001-Lead-Auditor 中文 Questions & Answers as PDF & Test Engine

Updated: Nov 15, 2026
No. of Questions: 418 Questions & Answers with Testing Engine
Download Limit: Unlimited
Instant Download: Upon successful payment, Our systems will automatically send the product you have purchased to your mailbox by email. (If not received within 12 hours, please contact us. Note: don't forget to check your spam.)
100% Money Back Guarantee
ActualVCE has an unprecedented 99.6% first time pass rate among our customers.  We're so confident of our products that we provide no hassle product exchange.
- Best exam practice material
- Three formats are optional
- 10 years of excellence
- 365 Days Free Updates
- Learn anywhere, anytime
- 100% Safe shopping experience


There is no waiting period at ActualVCE. Once your order is placed, the ISO-IEC-27001-Lead-Auditor 中文 practice questions for the PECB Certified ISO/IEC 27001 Lead Auditor exam (ISO-IEC-27001-Lead-Auditor中文版) arrive in your mailbox within a minute, and you can install the material on as many computers as you need.
PECB ISO-IEC-27001-Lead-Auditor 中文 Exam Overview:
| Certification Vendor: | PECB |
|---|---|
| Exam Name: | PECB Certified ISO/IEC 27001 Lead Auditor Exam |
| Exam Number: | ISO-IEC-27001-Lead-Auditor |
| Exam Format: | Multiple choice questions, Scenario-based questions |
| Exam Price: | $450 USD |
| Real Exam Qty: | 60 |
| Related Certifications: | PECB Certified ISO/IEC 27001 Lead Implementer PECB Certified ISO/IEC 27001 Foundation |
| Available Languages: | Portuguese, German, French, English, Spanish, Italian |
| Passing Score: | 70% |
| Exam Duration: | 120 minutes |
| Certificate Validity Period: | 3 years |
| Recommended Training: | PECB ISO/IEC 27001 Lead Auditor Training Course |
| Exam Registration: | PECB Official Exam Registration |
| Sample Questions: | DOWNLOAD DEMO |
| Exam Way: | Online proctored or onsite at authorized exam centers |
| Pre Condition: | Completion of PECB-certified ISO/IEC 27001 Lead Auditor training course; recommended prior knowledge of information security management systems and audit principles |
| Official Syllabus URL: | https://pecb.com/en/exam/iso-iec-27001-lead-auditor |
PECB ISO-IEC-27001-Lead-Auditor 中文 Exam Syllabus Topics:
| Section | Weight | Objectives |
|---|---|---|
| Topic 1: Auditing Principles and Practices | 30% | - Audit execution
|
| Topic 2: Requirements of ISO/IEC 27001:2022 | 30% | - General requirements and ISMS scope definition
|
| Topic 3: Information Security Controls (ISO/IEC 27002:2022) | 25% | - Control categories and implementation guidance
|
| Topic 4: Fundamental Concepts of Information Security | 15% | - Information security principles and definitions
|
Common Questions About the PECB Certified ISO/IEC 27001 Lead Auditor exam (ISO-IEC-27001-Lead-Auditor中文版) Exam
The PECB Certified ISO/IEC 27001 Lead Auditor exam (ISO-IEC-27001-Lead-Auditor中文版) (exam code ISO-IEC-27001-Lead-Auditor 中文) is the exam you pass to earn the PECB Certified ISO/IEC 27001 Lead Auditor certification, a credential at the Professional level. It is also connected with related credentials such as PECB Certified ISO/IEC 27001 Foundation, PECB Certified ISO/IEC 27001 Lead Implementer. If you are mapping out a certification path with PECB, this exam is a milestone worth planning around.
The ISO-IEC-27001-Lead-Auditor 中文 exam includes 60 questions, and you have 120 minutes to complete them. With that many questions on the clock, pacing is part of the challenge: divide your time into rough blocks as you go, and flag the items that stall you so you can circle back at the end instead of burning minutes on a single question. A week or two before your exam date, sit at least one full timed session in the ActualVCE test engine under the same time limit, so the pace feels familiar rather than frantic on the day.
You need 70% to pass the ISO-IEC-27001-Lead-Auditor 中文 exam, and the official registration fee is $450 USD. That fee is due again in full for every retake, which makes thorough preparation the cheaper investment by far. Before you book your seat, test yourself with the ActualVCE practice questions until you are scoring comfortably above the passing mark on a consistent basis — it is the simplest way to avoid paying for the same exam twice.
Completion of PECB-certified ISO/IEC 27001 Lead Auditor training course; recommended prior knowledge of information security management systems and audit principles
Eligibility rules can be adjusted by PECB over time, so before you register, confirm the current requirements on the official exam page: view the official ISO-IEC-27001-Lead-Auditor 中文 exam information.
You can book the ISO-IEC-27001-Lead-Auditor 中文 exam through the official registration channels below:
How the exam is taken: Online proctored or onsite at authorized exam centers.
PECB lists the following official training options for candidates preparing for this exam:
Once you have worked through the training, measure your readiness with the 418 practice questions from ActualVCE — they show you exactly which topics still need attention before you book the exam.
Yes. ActualVCE offers a free PDF demo of the ISO-IEC-27001-Lead-Auditor 中文 practice questions, so you can judge the quality of the material firsthand before paying anything. Every purchase also includes 365 days of free updates — if PECB changes the exam during that year, your material changes with it. And when the free update period expires, you can extend it at a 50% discount from within your member zone.
Every ISO-IEC-27001-Lead-Auditor 中文 purchase at ActualVCE is backed by a 100% Money Back Guarantee: if you take the corresponding exam within 60 days of your purchase and do not pass, you can apply for a full refund. The guarantee has clear conditions — it does not apply if you sit the exam within 3 days of purchase, if you downloaded the material but never actually took the exam, or to free materials and expired orders, and the candidate name must match the payer name. To file a claim, send a scan of your exam enrollment slip together with your official Score Report PDF within 2 days of the exam; claims are processed within 7 days. If you would rather not take a refund, you can exchange the product instead and receive two additional exam preparation products of equal value for free, while your original product keeps its update service. Delivery itself is instant: your material is available for download right after payment and is also sent to your email within one minute — if it has not arrived within 2 hours, contact our customer service. There is no limit on how many computers you can install it on.
The official PECB Certified ISO/IEC 27001 Lead Auditor exam (ISO-IEC-27001-Lead-Auditor中文版) outline divides the exam content into 4 main domains. The first three are:
- Requirements of ISO/IEC 27001:2022 — 30%
- Information Security Controls (ISO/IEC 27002:2022) — 25%
- Fundamental Concepts of Information Security — 15%
That is only the headline view — scroll back up to the Exam Topics section on this page for the complete domain-by-domain breakdown before you plan your study schedule.
PECB Certified ISO/IEC 27001 Lead Auditor exam (ISO-IEC-27001-Lead-Auditor中文版) Sample Questions:
下列敘述中哪兩項是正確的?
* 資訊安全管理系統認證的好處是在網站上展示認證證書。
- A. 資訊安全管理系統 (ISMS) 的目的是為了證明管理階層對資訊安全問題的認知。
- B. ISMS 的目的在於證明符合監管要求。
- C. 資訊安全管理系統 (ISMS) 的目的是應用風險管理流程來維護資訊安全。
- D. ISMS 認證的好處是增加客戶數量。
- E. 實施資訊安全管理系統的好處主要來自於降低資訊安全風險。
Correct Answer: B,C 🗳️
Explanation: Only visible for ActualVCE members. You can sign-up / login (it's free).
選擇最能完成下面句子的字詞來描述審計資源: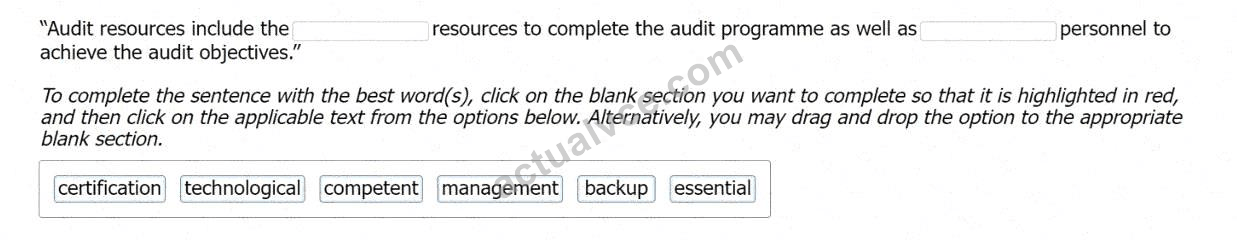
Correct Answer:
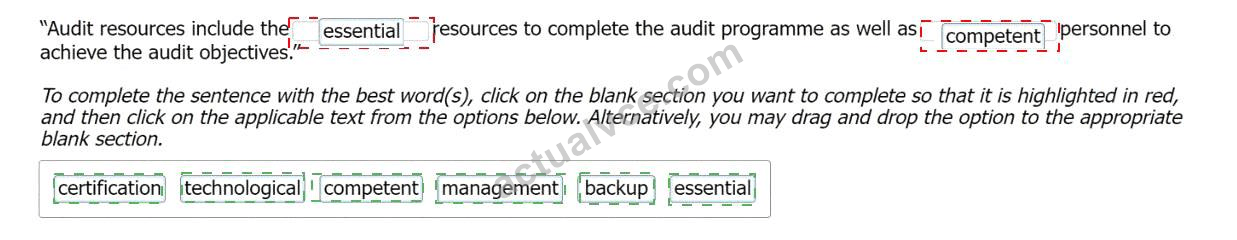
Explanation:
According to ISO 19011:2018, clause 5.3, the person responsible for managing the audit programme should determine the resources necessary for the audit programme, such as the audit team members, the budget, the time, the tools, etc. The audit resources should be sufficient and appropriate to ensure the quality and effectiveness of the audit programme and the audit results. The audit resources include the following elements12:
* Essential resources: These are the resources that are required to conduct the audit programme and the individual audits, such as the audit documents, the audit methods, the audit tools, the audit schedule, the audit budget, etc. The essential resources should be identified and allocated based on the audit objectives, scope, and criteria, and the availability and cooperation of the auditee. The essential resources should also be reviewed and updated as necessary to reflect any changes or deviations in the audit programme or the individual audits.
* Competent personnel: These are the audit team members who have the appropriate knowledge, skills, and experience to conduct the audit effectively and efficiently, and to provide credible and reliable audit results and recommendations. The competent personnel should include the audit team leader, the auditors, and any technical experts or observers who support the audit team. The competent personnel should be selected and appointed based on the audit objectives, scope, and criteria, and the specific competence requirements for the audit programme and the individual audits. The competent personnel should also be independent and impartial, and avoid any conflicts of interest or self-interest that may affect the audit results or the audit decisions.
References:
ISO 19011:2018 - Guidelines for auditing management systems, clause 5.3 PECB Candidate Handbook ISO 27001 Lead Auditor, page 19
情境7
Lawsy是一家領先的律師事務所,在泰國曼谷設有辦事處。它擁有50多名律師,為客戶提供商業法、智慧財產權、銀行和金融服務等領域的專業法律服務。
他們相信,憑藉對資訊安全最佳實踐的貫徹落實以及對技術發展的持續關注,他們在市場上擁有穩固的地位。
兩年來,Lawsy 一直嚴格執行、評估並進行資訊安全管理系統 (ISMS) 的內部審核。現在,他們已向知名且值得信賴的認證機構 ISMA 申請 ISO/IEC 27001 認證。
在第一階段審核中,審核團隊審查了實施階段所創建的所有資訊安全管理系統(ISMS)文件。他們還審查並評估了管理評審和內部審核的記錄。 Lawsy提交的證據記錄表明,在必要時已對不符合項採取了糾正措施,因此審核團隊對內部審核員進行了訪談。訪談透過深入了解內部審核計畫和程序,驗證了內部審核的充分性和頻率。
審計團隊繼續核實策略文件,包括資訊安全政策和風險評估標準。在資訊安全政策審查過程中,團隊發現已記錄的治理框架資訊與實際操作流程有不一致之處。第一階段完成後,審計團隊負責人制定了審計計劃,其中涵蓋了審計目標、範圍、標準和流程。
在第二階段審計中,審計團隊採訪了資訊安全經理,他負責起草資訊安全政策。他解釋說,Lawsy 每三個月都會進行強制性的資訊安全培訓和意識提升活動,以此來解釋第一階段發現的問題。
審計小組隨後發現,儘管勞西公司允許員工將筆記型電腦帶出工作場所,但該公司並未制定在工作場所外使用筆記型電腦的相關程序。該公司僅提供關於筆記型電腦使用的一般性信息,並依賴員工的常識來保護儲存在筆記型電腦上的資訊的機密性和完整性。
面談結束後,審核小組審查了15份員工培訓記錄(共50份),並得出結論:Lawsy符合ISO/IEC 27001關於培訓和意識方面的要求。為佐證該結論,審核員在審核結束後對審查的員工培訓記錄進行了複印和存檔。
問題
Lawsy公司沒有關於在工作場所外使用筆記型電腦的規章制度,而是依靠員工的常識來保護儲存在筆記型電腦上的資訊的機密性。這會帶來什麼問題?
- A. 不符合
- B. 異常
- C. 一致性
Correct Answer: A 🗳️
Explanation: Only visible for ActualVCE members. You can sign-up / login (it's free).
情境 5:Data Grid Inc. 是一家知名公司,為整個資訊科技基礎設施提供安全服務。它提供網路安全軟體,包括端點安全、防火牆和防毒軟體。二十年來,Data Grid Inc. 透過先進的產品和服務幫助多家公司保護其網路安全。 Data Grid Inc. 在資訊和網路安全領域享有盛譽,決定獲得 ISO/IEC 27001 認證,以更好地保護其內部和客戶資產並獲得競爭優勢。
Data Grid Inc. 任命了審計團隊,該團隊同意審計任務的條款。此外,Data Grid Inc.明確了審核範圍,明確了審核標準,並建議在五天內結束審核。由於Data Grid Inc.員工人數眾多,流程複雜,審計小組拒絕了Data Grid Inc.在五天內進行審計的提議。 Data Grid Inc.堅稱他們計劃在五天內完成審核,因此雙方同意在規定的時間內進行審核。審計小組遵循基於風險的審計方法。
為了獲得主要業務流程和控制的概述,審計團隊存取了流程描述和組織圖表。他們無法對 IT 風險和控制進行更深入的分析,因為他們對 IT 基礎架構和應用程式的存取受到限制。然而,審計小組表示,Data Grid Inc. 的 ISMS 出現重大缺陷的風險很低,因為該公司的大部分流程都是自動化的。因此,他們透過詢問 Data Grid Inc. 的代表以下問題來評估 ISMS 整體上符合標準要求:
*如何定義和指派 IT 和 IT 控制的職責?
*Data Grid Inc. 如何評估控制措施是否達到了預期效果?
*Data Grid Inc. 採取了哪些控制措施來保護操作環境和資料免受惡意軟體的侵害?
*是否實施了與防火牆相關的控制?
Data Grid Inc. 的代表提供了充分且適當的證據來解決所有這些問題。
審計組長起草審計結論並向Data Grid Inc. 的最高管理階層報告。
儘管審核員推薦Data Grid Inc.進行認證,但Data Grid Inc.與認證機構之間在審核目標方面產生了誤解。 Data Grid Inc. 表示,儘管審計目標包括確定潛在改進的領域,但審計團隊並未提供此類資訊。
根據該場景,回答以下問題:
Data Grid Inc. 對以下所有行為負責,但以下情況除外:
- A. 定義審核範圍
- B. 指定審核標準
- C. 任命審核團隊
Correct Answer: C 🗳️
Explanation: Only visible for ActualVCE members. You can sign-up / login (it's free).
情境 3
NightCore是一家總部位於美國的跨國科技企業,專注於電子商務、雲端運算、數位串流媒體和人工智慧(AI)。在實施資訊安全管理系統(ISMS)一年多後,NightCore委託一家認證機構進行ISO/IEC 27001認證審核。
認證機構組建了一支由五名審核員組成的團隊,傑克擔任團隊負責人。傑克在風險管理、資訊安全控制和事件管理方面擁有豐富的審核經驗,並因此而聞名。
他的技能與審計原則和流程的要求高度契合,使他能夠有效理解審計範圍並有效運用相關標準。傑克也展現出對NightCore的組織結構、宗旨和管理實踐以及適用於其業務活動的法律法規要求的深刻理解。
審計團隊遵循合理的審計方法,系統性地得出可靠且可重複的結論。審計團隊認識到,只有能夠在一定程度上核實的資訊才能被視為有效證據。在審計過程中,極少數情況下,如果某些資訊的核實存在困難且其可核實程度較低,審計人員會運用專業判斷來評估此類證據的可靠性,並確定其可信度。
在審計過程中,審計人員記錄了他們對NightCore資訊安全管理系統(ISMS)運作規劃和控制的觀察結果和檢查筆記。他們也記錄了對NightCore資訊清單及相關資產的觀察結果。此外,審計人員也審查了為保護網路服務連線而實施的防火牆配置。
隨著審核進入最後階段,NightCore對維護最高資訊安全標準的承諾日益凸顯。憑藉著觸手可及的ISO/IEC 27001認證,NightCore已做好充分準備,有望獲得該認證,從而提升其在科技行業的聲譽。
問題
在對NightCore進行審計期間,審計人員重點關注了資訊安全管理系統(ISMS)營運的關鍵領域,包括營運規劃、資產清單和防火牆配置。審計人員在對NightCore進行的審計中收集了哪些類型的證據?
- A. 數學證據
- B. 分析與文獻證據
- C. 實物與技術證據
Correct Answer: C 🗳️
Explanation: Only visible for ActualVCE members. You can sign-up / login (it's free).
Viewing page 1 out of 84 pages.
Viewing questions 1-5 out of 418 questions.
 0 Customer ReviewsCustomers Feedback (* Some similar or old comments have been hidden.)
Instant Download ISO-IEC-27001-Lead-Auditor 中文
After Payment, our system will send you the products you purchase in mailbox in a minute after payment. If not received within 2 hours, please contact us.
365 Days Free Updates
Free update is available within 365 days after your purchase. After 365 days, you will get 50% discounts for updating.

Money Back Guarantee
Full refund if you fail the corresponding exam in 60 days after purchasing. And Free get any another product.
Security & Privacy
We respect customer privacy. We use McAfee's security service to provide you with utmost security for your personal information & peace of mind.
