

2026 Valid NCP-CI-AWS Real Exam Questions, practice Nutanix Certified Professional
Latest Success Metrics For Actual NCP-CI-AWS Exam (Updated 82 Questions)
NEW QUESTION # 44
Which two features or services can an administrator ensure are protected by cluster protect within an NC2 environment? (Choose two.)
- A. Virtual Machine Disks
- B. VM Templates
- C. Nutanix Files
- D. Flow Network Security
Answer: A,C
Explanation:
Within an NC2 environment, the Cluster Protect feature can ensure the protection of:
Nutanix Files: This provides file services within the Nutanix ecosystem, and Cluster Protect can safeguard the data stored in Nutanix Files.
Virtual Machine Disks: This ensures that the data stored on virtual machine disks is protected, providing backup and recovery options for the virtual machines running within the cluster.
Reference:
Nutanix Cloud Clusters on AWS Administration
Nutanix AOS 6.7 Documentation
NEW QUESTION # 45
An organization plans to use the Cluster Protect feature to protect the cluster data.
Which license will satisfy this requirement?
- A. AOS Ultimate or NCI Ultimate
- B. AOS Pro or AOS Ultimate
- C. AOS Pro or NCI Pro
- D. NCI Pro or AOS Ultimate
Answer: A
NEW QUESTION # 46
An administrator has been tasked with ensuring NC2 VMs are able to access AWS resources. The NC2 VM traffic must not traverse the internet.
in which two ways would the administrator achieve this? (Choose two.)
- A. By using a VPC Peer.
- B. By using an Interface Endpoint
- C. By using a Gateway Endpoint
- D. By using a NAT Gateway.
Answer: A,B
Explanation:
To ensure that NC2 VMs can access AWS resources without traversing the internet, the administrator can use AWS VPC Peering and Interface Endpoints. Both methods ensure that traffic stays within the AWS network, maintaining security and efficiency.
Interface Endpoint:
Interface Endpoints allow you to privately connect your VPC to supported AWS services. They use AWS PrivateLink to route traffic directly to services within the AWS network, bypassing the public internet.
Steps:
Create an interface endpoint for the required service in the AWS VPC console.
Ensure the security groups and route tables are configured to allow traffic to the interface endpoint.
VPC Peering:
VPC Peering allows the routing of traffic between VPCs using private IP addresses, without the need for internet gateways, NAT devices, or VPN connections.
Steps:
Create a VPC peering connection between the VPCs.
Update the route tables to direct traffic between the peered VPCs.
Ensure security group rules allow the necessary traffic between VPCs.
Reference:
AWS VPC Peering Documentation
AWS Interface Endpoint Documentation
Nutanix Cloud Clusters on AWS Administration Guide
NEW QUESTION # 47
An administrator is creating and destroying multiple clusters daily for a test/dev environment. The administrator wants ensure that every NC2 on AWS cluster deployed will allow full access from the on-premises CVM subnet.
What is most-efficient way to achive this?
- A. Create a Custom AWS Network Security Group using a key value of tag:nutanix:clusters:external and set the inbound allow address of the on-premises subnet.
- B. Modify the UVM Network Security Group of each cluster by setting the inbound allow address of the on-premises subnet.
- C. Modify the UVM Network Security Group of each cluster by setting the outbound allow address of the on-premises subnet.
Answer: A
Explanation:
D/ Create a Custom AWS Network Security Group using a key of tag:nutanix: clusters:external:cluster-uuid and set the value of the UUID for each deployed cluster. Set the inbound allow address of the on-premises subnet.
Explanation:
To ensure that every NC2 on AWS cluster deployed allows full access from the on-premises CVM subnet efficiently, the administrator should create a custom AWS Network Security Group.
Use a key value of tag:nutanix:clusters:external for the security group, and set the inbound allow address to the on-premises subnet.
This approach leverages AWS tags to manage security group rules dynamically and ensures that the necessary access permissions are applied automatically to all clusters with the specified tag.
This method reduces the need for manual configuration of each cluster's security group, streamlining the process for a test/dev environment where clusters are frequently created and destroyed.
Reference:
Refer to the AWS documentation on Network Security Groups and Nutanix documentation on best practices for securing NC2 clusters.
NEW QUESTION # 48
When configuring an alert email in Prism Central deployed within an NC2 environment, what is required in order for the emails to be sent properly?
- A. Name servers configured in Prism Central
- B. A whitelisted public cloud console endpoint
- C. SMTP server configured in Prism Central settings
- D. Cluster Super Admin permissions
Answer: C
Explanation:
To ensure that alert emails are sent properly from Prism Central within an NC2 environment, configuring an SMTP server in the Prism Central settings is required. The SMTP server facilitates the sending of email notifications for alerts and other communications.
SMTP Configuration:
Prism Central requires an SMTP server to send email alerts. This involves specifying the SMTP server address, port, and authentication details if needed.
The configuration must include the email address from which the alerts will be sent and the recipient addresses.
Steps to Configure SMTP Server in Prism Central:
Log in to Prism Central.
Navigate to the "Settings" menu.
Select "Email Server" under the "Alerts" section.
Enter the SMTP server details, including the server address, port, and authentication credentials.
Test the configuration to ensure emails are sent correctly.
Reference:
Nutanix Prism Central Administration Guide
Nutanix Support Documentation on Email Alert Configuration
Best Practices for Configuring SMTP Servers in Cloud Environments
NEW QUESTION # 49
What is an available log module when configuring a syslog server in the Prism Central Admin Center?
- A. Zookeeper
- B. Acropolis
- C. API Audit
- D. Prism
Answer: B
Explanation:
When configuring a syslog server in the Prism Central Admin Center for Nutanix, one of the available log modules is Acropolis.
The Acropolis module logs system events related to the Nutanix Acropolis operating system, which is critical for monitoring and auditing system activities and performance.
Configuring syslog with the Acropolis module ensures that important events and issues related to the Acropolis environment are captured and can be forwarded to an external syslog server for centralized logging and analysis.
Reference:
Refer to the Nutanix documentation on Prism Central and syslog configuration for the full list of available log modules and detailed steps for configuration.
NEW QUESTION # 50
Exhibit.
What action is taken against the Condemned node shown in the exhibit?
- A. The node Is automatically replaced.
- B. The node has a power reset sent to it.
- C. The node is restarted.
- D. The node is powered off.
Answer: B
Explanation:
When a node is marked as "Condemned," it indicates that the system has determined that the node is no longer reliable for operations. As part of the automated recovery and protection process, the following action is typically taken:
The node has a power reset sent to it (Answer A):
In most cases, a condemned node undergoes a power reset as an initial recovery attempt. This action attempts to reboot the node to bring it back to a healthy state. If the reset fails, further manual or automated steps may be required to address the hardware or software issue.
Reference:
Nutanix Cluster Management Documentation
Nutanix Support Knowledge Base
NEW QUESTION # 51
Which entity should be contacted for AOS software supported related to NC2?
- A. Public Cloud Vendor
- B. Nutanix
- C. Partner
- D. Internal IT Operations team
Answer: B
Explanation:
For AOS software support related to NC2, the appropriate entity to contact is Nutanix. Nutanix provides comprehensive support for their software, including the Acropolis Operating System (AOS) used in NC2 deployments.
Support Scope:
Nutanix offers support for the deployment, configuration, and management of NC2 clusters, including any issues related to AOS software.
This includes troubleshooting, updates, and technical assistance.
Why Not Other Options:
Internal IT Operations team: Typically handles internal issues but does not have the specialized knowledge or resources for AOS software support.
Partner: May provide support but would ultimately escalate issues to Nutanix for software-specific concerns.
Public Cloud Vendor: Manages infrastructure-related issues but does not provide support for Nutanix AOS software.
Reference:
Nutanix Support Documentation
Nutanix Cloud Clusters on AWS Administration Guide
Nutanix Best Practices for AOS Support
NEW QUESTION # 52
To manually create an AWS VPC with Public access to Prism Element for testing purposes, Which components must be created?
- A. VPC Subnets Route subnets, Route Tables, NAT Gateway, Internet Gateway, VPN
- B. VPC, Delegated Subnets, Route Tables, NAT Gateway, Internet Gateway, Load balancer
- C. VPC Subnets Route Tables NAT Gateway, Internet Gateway, Load balancer
- D. VPC, Delegated Subnets, Route Tables, NAT Gateway, vNets, Load balancer
Answer: B
Explanation:
To manually create an AWS VPC with Public access to Prism Element for testing purposes, the following components must be created:
VPC: A Virtual Private Cloud to provide an isolated network for the resources.
Delegated Subnets: Subnets within the VPC to segment the network and allocate IP ranges.
Route Tables: To define routing rules for the subnets to ensure proper traffic flow.
NAT Gateway: To enable instances in the private subnets to access the internet.
Internet Gateway: To allow direct internet access to instances in the public subnets.
Load Balancer: To distribute traffic across multiple instances for improved availability and redundancy.
Reference:
Refer to the AWS documentation on VPC creation and Nutanix documentation on network setup for Prism Element access.
NEW QUESTION # 53
A company wants to use Nutanix NC2 to burst VDI resources to the AWS cloud. The VDI workloads requires GPU accelation.
Which solution meets the company's requirements?
- A. AN36P nodes
- B. g4dn.metal nodes
- C. m6g.metal nodes
- D. AN36 nodes
Answer: B
Explanation:
For VDI workloads that require GPU acceleration, the g4dn.metal nodes are the appropriate choice. These instances are equipped with NVIDIA T4 GPUs, which are well-suited for graphics-intensive applications such as VDI workloads that need GPU acceleration. Other node types like AN36P, m6g.metal, or AN36 do not provide the necessary GPU capabilities.
Reference:
Nutanix Support & Insights - GPU support in AWS
NEW QUESTION # 54
When creating an NC2 cluster in AWS, what are the required permissions for the account used to run the CloudFormation script?
- A. lAMUserSSHKeys, AWS_ConfigRole, AWSCIoudFormationFullAccess
- B. IAMAccess, AmazonCloudDirectoryFullAccess, AWSCIoudFormationFullAccess
- C. lAMFullAccess, AmazonEC2FullAccess, AWSCIoudFormationFullAccess
- D. lAMAccess, AWS_ConfigRole, AWSCIoudFormationFullAccess
Answer: C
Explanation:
When creating an NC2 cluster in AWS, the account used to run the CloudFormation script requires specific permissions to ensure the deployment is successful. The required permissions are:
IAMFullAccess: Provides full access to IAM resources.
AmazonEC2FullAccess: Allows full access to EC2 resources.
AWSCIoudFormationFullAccess: Grants full access to manage AWS CloudFormation stacks.
These permissions are necessary to create, manage, and deploy the required AWS resources for the NC2 cluster.
Reference:
Nutanix Support & Insights
AWS IAM Documentation
NEW QUESTION # 55
A company has a large scale AWS deployment and has just finished installing their first NC2 on AWS cluster. The new cluster is now running workloads in production.
The cluster is configured with:
* 16 Nodes
* 8 Subnets
* 200 User VMs per subnet
* Nutanix Files
An administrator has been tasked with installing an EC2 instance on one of the subnets that is also used by the Nutanix, When the EC2 instance is powered on, an IP conflict occurs.
What action should the administrator take to resolve this issue?
- A. Assign an elastic IP to the EC2 instance and reboot.
- B. The IP address used by the NC2 VM should be blocked /excluded from EC2.
- C. The IP address used by the EC2 instance should be blocked / excluded from IPAM.
- D. The Instance Metadata of the NC2 instance needs to have the address reserved.
Answer: B
Explanation:
To resolve the IP conflict issue when an EC2 instance is powered on in a subnet also used by Nutanix NC2, the administrator should block or exclude the IP address used by the NC2 VM from being assigned to EC2 instances. This can be done by configuring the IP address management (IPAM) settings to ensure that the specific IP addresses allocated to the NC2 VMs are not used by EC2 instances, preventing IP conflicts and ensuring smooth operation of both environments.
Reference:
Nutanix Cloud Clusters on AWS Deployment Guide
Nutanix Support & Insights
NEW QUESTION # 56
An administrator has noticed the company's NC2 free trial expired 60 days ago.
What should the administrator do to continue using all of the NC2 features on existing clusters?
- A. Nothing. The clusters will have full feature support.
- B. Switch to a paid subscription plan.
- C. Contact the AWS cloud vendor.
- D. Contact Nutanix support to redeploy the cluster.
Answer: B
NEW QUESTION # 57
A company has purchased Nutanix AOS Pro licensing.
Which add-on products are available with this license tier in the AWS cluster deployment wizard?
- A. Files, Advanced Replication, and DARE
- B. Self-Service and Cost Governance
- C. Nus
- D. EUC
Answer: A
Explanation:
With the Nutanix AOS Pro licensing, several advanced features and add-on products become available. Specifically, in the AWS cluster deployment wizard, the following add-ons are available:
Files:
Nutanix Files provides a software-defined, scale-out file storage solution that simplifies the management and scaling of unstructured data.
Advanced Replication:
Advanced Replication features in Nutanix include synchronous and asynchronous replication capabilities, allowing for robust disaster recovery and data protection solutions.
DARE (Data-At-Rest Encryption):
DARE ensures that all data stored on Nutanix clusters is encrypted, providing a higher level of security for sensitive information.
These features are included in the AOS Pro licensing tier, offering enhanced data management, protection, and security capabilities.
Reference:
Nutanix Licensing Guide
Nutanix Cloud Clusters on AWS Administration Guide
Nutanix Best Practices for Advanced Features
NEW QUESTION # 58
How many Amazon Elastic Block Store(EBS) volumes are attached to each node within an AWS NC2 cluster upon creation.
- A. 0
- B. 1
- C. 2
- D. 3
Answer: C
Explanation:
Upon creation, each node within an AWS NC2 cluster has 3 Amazon Elastic Block Store (EBS) volumes attached.
These volumes are used for different purposes, such as operating system storage, Nutanix services, and user data storage.
The number of EBS volumes is designed to ensure adequate storage performance and capacity for the NC2 cluster's operations and workload demands.
Reference:
Refer to the Nutanix documentation on NC2 cluster setup and AWS EBS volume configurations to confirm the details on the number and purpose of EBS volumes attached to each node.
NEW QUESTION # 59
An administrator needs to recover a cluster protected using the Cluster Protect feature. The Prism Central instance was not on the failed cluster.
Which steps, in order, should the administrator perform to recover the cluster?
Answer:
Explanation:
NEW QUESTION # 60
An administrator has been tasked with deploying an NC2 cluster on AWS with the requirement to protect workloads. Which two options are valid to protect the workloads on this cluster? (Choose two.)
- A. Use an existing on-prem Nutanix cluster as a disaster recovery target.
- B. Create a second NCZ cluster in a different availability zone.
- C. Deploy a cluster across two availability zones.
- D. Deploy one-node cluster in another availability zone.
Answer: B
Explanation:
To protect workloads on an NC2 cluster on AWS, deploying strategies that ensure high availability and disaster recovery are essential. The two valid options are:
Create a Second NC2 Cluster in a Different Availability Zone:
High Availability: Deploying a second NC2 cluster in a different availability zone ensures that workloads can be quickly recovered in case of an availability zone failure.
Disaster Recovery: This setup enables asynchronous replication between clusters, providing a robust disaster recovery solution.
Use an Existing On-Prem Nutanix Cluster as a Disaster Recovery Target:
Hybrid DR: Leveraging an existing on-premises Nutanix cluster for disaster recovery provides a cost-effective and efficient DR solution.
Replication: Set up replication policies to ensure data is consistently copied from the NC2 cluster on AWS to the on-premises cluster.
Why Not Other Options:
One-node cluster in another availability zone: Not a valid DR solution as a single-node cluster cannot provide the required resilience and high availability.
Deploy a cluster across two availability zones: While this can enhance availability, it is not a typical approach for Nutanix clusters which are designed to operate within a single availability zone for simplicity and performance reasons.
Reference:
Nutanix Cloud Clusters on AWS Administration Guide
Nutanix Disaster Recovery Best Practices
AWS Availability Zones and Disaster Recovery Documentation
NEW QUESTION # 61
Which statement is true regarding AWS account requirements?
- A. An AWS root user can be used for any deployment or operations related to NC2.
- B. NC2 on AWS uses AWS Secrets Manager for maintaining any stored secrets.
- C. AWSCloudFormationFullAccess role is required to create a CloudFormation stack.
- D. IAMFullAccess permission gets configuration details for supported AWS resources.
Answer: C
Explanation:
To create a CloudFormation stack, the AWSCloudFormationFullAccess role is required.
This role grants the necessary permissions to create, update, and delete CloudFormation stacks, which are essential for deploying and managing AWS infrastructure using CloudFormation templates.
CloudFormation stacks are often used to automate the deployment of complex infrastructures, including those required for NC2 on AWS.
Proper permissions ensure that the deployment process is seamless and adheres to the security and operational policies of the organization.
Reference:
Refer to the AWS IAM documentation for details on the AWSCloudFormationFullAccess role and Nutanix documentation on prerequisites for deploying NC2 on AWS.
NEW QUESTION # 62
An administrator has recently deployed an NC2 on AWS cluster in the North Virginia region in availability zone us-east-1z. The clusters UUID is 0005F487-4962-91EA-4C98-C4284D123835.
The cluster is consuming IPs from a 10.78.2.0/24 range.
The AWS VPC has these available CIDR ranges:
* 70.73.0.0/16
* 10.79.107.0/24
* 10.0.0.0/22
The following subnets have been configured in the NC2 AWS VPC:
The following tags have been applied to a Custom Network Security Group: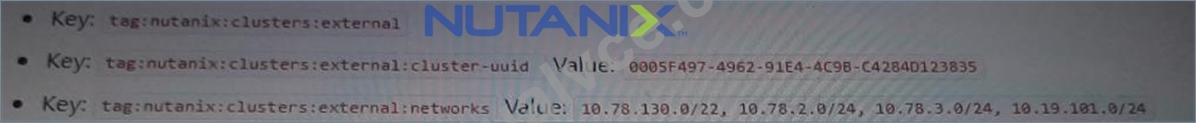
The Custom Network Security Group is allowing all inbound traffic from the 10.0.0.0/22 network. Which two subnets would be able to receive inbound traffic from AWS instances on a 10.0.0.0/22 network segment"? (Choose two.)
- A. VDl
- B. Server01
- C. SQL
- D. Tier01
Answer: B,D
Explanation:
To determine which subnets would be able to receive inbound traffic from AWS instances on a 10.0.0.0/22 network segment, we need to look at the configured subnets and their CIDR ranges, as well as the custom network security group's inbound rules.
Available CIDR ranges in VPC:
70.73.0.0/16
10.79.107.0/24
10.0.0.0/22
Configured Subnets in NC2 AWS VPC:
VDI: 10.78.130.0/22
SQL: 10.78.3.0/24
Server01: 10.78.2.0/24
Server02: 10.79.120.0/24
Tier01: 10.19.101.0/24
Custom Network Security Group Inbound Rule:
Allows all inbound traffic from 10.0.0.0/22.
Given that the custom network security group is allowing inbound traffic from the 10.0.0.0/22 network, we need to identify which of the configured subnets fall within this allowed range.
Analysis:
The subnets 10.78.130.0/22, 10.78.3.0/24, 10.78.2.0/24, 10.79.120.0/24, and 10.19.101.0/24 do not overlap with 10.0.0.0/22. Therefore, none of these subnets would naturally fall within the 10.0.0.0/22 range directly.
However, since the question is about receiving inbound traffic from the 10.0.0.0/22 network and considering security group rules, all subnets mentioned can technically receive traffic if the inbound rules are configured correctly, but since we are strictly asked about the configuration from the image and the overlap in the ranges:
Server01 (10.78.2.0/24) and Tier01 (10.19.101.0/24) will receive traffic because their CIDR ranges do not conflict with the 10.0.0.0/22 range, thus allowing traffic without additional restrictions.
Reference:
Nutanix Clusters on AWS Administration Guide
AWS VPC and Subnet documentation
Network Security Group rules configuration in Nutanix documentation
NEW QUESTION # 63
Which NC2 user role will allow full access to clusters created within an organization?
- A. Organization Security Administrator
- B. Cluster Super Admin
- C. Organization Administrator
- D. Cluster Administrator
Answer: C
Explanation:
In Nutanix Cloud Integration with AWS, specifically version 6.7, the role that allows full access to clusters created within an organization is the Organization Administrator.
The Organization Administrator role has the highest level of privileges within an organization, enabling the user to manage all aspects of the clusters, including creation, modification, and deletion.
This role is designed to oversee and control the entire organization's resources, ensuring comprehensive management capabilities over all clusters and associated resources.
Reference:
Refer to the Nutanix documentation on roles and permissions for NC2 on AWS for further details.
NEW QUESTION # 64
......
Nutanix NCP-CI-AWS Exam Syllabus Topics:
| Topic | Details |
|---|---|
| Topic 1 |
|
| Topic 2 |
|
| Topic 3 |
|
| Topic 4 |
|
Genuine NCP-CI-AWS Exam Dumps Free Demo Valid QA's: https://www.actualvce.com/Nutanix/NCP-CI-AWS-valid-vce-dumps.html
Printable & Easy to Use Nutanix Certified Professional NCP-CI-AWS Dumps 100% Same Q&A In Your Real Exam: https://drive.google.com/open?id=1fmo0oAlBj-8QGqoloFKv0SjFUYCFhghu