

100% Free MS-500 Files For passing the exam Quickly UPDATED Nov 01, 2022
MS-500 Dumps Questions Study Exam Guide
Difficulty in writing the Microsoft MS-500 Exam:
Due to the fact the Microsoft certification exams are computer-based tests, candidates can find it extremely difficult to write, especially those candidates who have been out of the field for a long time or those with little or no knowledge of the subject they are about to be tested on. Outdated content may lead the candidate to take the test more than once. The individual needs to practice writing many sample questions, and they need to know how to answer software development questions that have been previously asked on the MS-500 Exam. Requirements may vary from one exam to another. The multiple-choice format of these exams is not easy for most candidates and can cause them mental stress and difficulty understanding the test objective and answering the question correctly. MS-500 Dumps are commonly used to assist candidates in their preparation for the certification exams. The Microsoft certification exams are not only updated every year, but they also change their format. Any threat to safety can result in a loss of focus and concentration. Many candidates fear that they will forget some questions, so they abridge their answers by omitting irrelevant information, but this will only result in wasting valuable time and money on rescheduling exams that do not allow abridging test questions. Most candidates who fail these exams do not get the opportunity to get their results. Data is updated every five minutes, which will allow the candidate to track their progress. Workers can withdraw from the certification exam when they want.
NEW QUESTION 72
You have a Microsoft 365 subscription.
You create a retention label named Label1 as shown in the following exhibit.
You publish Label1 to SharePoint sites.
Use the drop-down menus to select the answer choice that completes each statement based on the information presented in the graphic.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation
References:
https://docs.microsoft.com/en-us/office365/securitycompliance/labels
NEW QUESTION 73
You have a Microsoft 365 subscription.
You identify the following data loss prevention (DLP) requirements:
Send notifications to users if they attempt to send attachments that contain EU social security numbers Prevent any email messages that contain credit card numbers from being sent outside your organization Block the external sharing of Microsoft OneDrive content that contains EU passport numbers Send administrators email alerts if any rule matches occur.
What is the minimum number of DLP policies and rules you must create to meet the requirements? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
NEW QUESTION 74
You have a Microsoft 365 subscription.
You need to ensure that all users who are assigned the Exchange administrator role have multi-factor authentication (MFA) enabled by default.
What should you use to achieve the goal?
- A. Security & Compliance permissions
- B. Microsoft Azure Active Directory (Azure AD) Privileged Identity Management
- C. Microsoft Office 365 user management
- D. Microsoft Azure AD group management
Answer: B
NEW QUESTION 75
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You have a Microsoft 365 subscription.
You have a user named User1. Several users have full access to the mailbox of User1.
Some email messages sent to User1 appear to have been read and deleted before the user viewed them.
When you search the audit log in Security & Compliance to identify who signed in to the mailbox of User1, the results are blank.
You need to ensure that you can view future sign-ins to the mailbox of User1.
You run the Set-AuditConfig -Workload Exchangecommand.
Does that meet the goal?
- A. Yes
- B. No
Answer: B
Explanation:
Explanation/Reference:
References:
https://docs.microsoft.com/en-us/powershell/module/exchange/policy-and-compliance-audit/set-auditconfig?
view=exchange-ps
NEW QUESTION 76
Your network contains an on-premises Active Directory domain named contoso.com. The domain contains the groups shown in the following table.
The domain is synced to a Microsoft Azure Active Directory (Azure AD) tenant that contains the groups shown in the following table.
You create an Azure Information Protection policy named Policy1.
You need to apply Policy1.
To which groups can you apply Policy1? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Reference:
https://docs.microsoft.com/en-us/azure/information-protection/prepare
NEW QUESTION 77
You need to create Group3.
What are two possible ways to create the group?
- A. a distribution list in the Microsoft 365 admin center
- B. an Office 365 group in the Microsoft 365 admin center
- C. a security group in the Azure AD admin center
- D. a security group in the Microsoft 365 admin center
- E. a mail-enabled security group in the Microsoft 365 admin center
Answer: A,B
Explanation:
Topic 3, Contoso, Ltd
Existing Environment
Infrastructure
The network contains an Active Directory domain named contoso.com that is synced to a Microsoft Azure Active Directory (Azure AD) tenant. Password writeback is enabled.
The domain contains servers that run Windows Server 2016. The domain contains laptops and desktop computers that run Windows 10 Enterprise.
Each client computer has a single volume.
Each office connects to the Internet by using a NAT device. The offices have the IP addresses shown in the following table.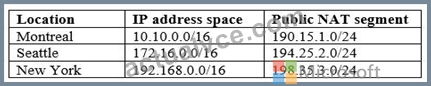
Named locations are defined in Azure AD as shown in the following table.
From the Multi-Factor Authentication page, an address space of 198.35.3.0/24 is defined in the trusted IPs list.
Azure Multi-Factor Authentication (MFA) is enabled for the users in the finance department.
The tenant contains the users shown in the following table.
The tenant contains the groups shown in the following table.
Customer Lockbox is enabled in Microsoft 365.
Microsoft Intune Configuration
The devices enrolled in Intune are configured as shown in the following table.
The device compliance policies in Intune are configured as shown in the following table.
The device compliance policies have the assignments shown in the following table.
The Mark devices with no compliance policy assigned as setting is set to Compliant.
Requirements
Technical Requirements
Contoso identifies the following technical requirements:
Use the principle of least privilege
Enable User1 to assign the Reports reader role to users
Ensure that User6 approves Customer Lockbox requests as quickly as possible Ensure that User9 can implement Azure AD Privileged Identity Management
NEW QUESTION 78
You need to create a policy that identifies content in Microsoft OneDrive that contains credit card numbers.
To complete this task, sign in to the Microsoft 365 portal.
Answer:
Explanation:
See explanation below.
Explanation
Youneed to configure auto-labeling in 'simulation' mode. In the policy, you can select the 'Credit Card' sensitive info type.
In the Microsoft 365 compliance center, navigate to sensitivity labels:
Solutions > Information protection
Select the Auto-labeling(preview) tab.
Select + Create policy.
For the page Choose info you want this label applied to: Select one of the templates, such as Financial or Privacy. You can refine your search by using the Show options for dropdown. Or, select Custom policy if the templates don't meet your requirements. Select Next.
For the page Name your auto-labeling policy: Provide a unique name, and optionally a description to help identify the automatically applied label, locations, and conditions that identify the content to label.
For the page Choose locations where you want to apply the label: Select OneDrive. Then select Next.
For the Define policy settings page: Keep the default of Find content that contains to define rules that identify content to label across all your selected locations. The rules use conditions that include sensitive information types and sharing options. For sensitive information types, you can select both built-in and custom sensitive information types.
Then select Next.
For the Set up rules todefine what content is labeled + Create rule and then select Next
.
On the Create rule page, name and define your rule, using sensitive information types and then select Save.
ClickNext.
For the Choose a label to auto-apply , select a label from the Choose a sensitivity label pane, and then select For the Decide if you want to run policy simulation now or later page: Select Run policy in simulation mode if you're ready to run the auto-labeling policy now, insimulation mode. Otherwise, select Leave policy turned off For the Summary page: Review the configuration of your auto-labeling policy and make any changes that needed, and complete the wizard.
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/apply-sensitivity-label-automatically?view=o365-w
NEW QUESTION 79
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some questions sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You have a Microsoft 365 subscription that contains the users shown in the following table.
You discover that all the users in the subscription can access Compliance Manager reports.
The Compliance Manager Reader role is not assigned to any users.
You need to recommend a solution to prevent a user named User5 from accessing the Compliance Manager reports.
Solution: You recommend removing User1 from the Compliance Manager Contributor role.
Does that meet the goal?
- A. Yes
- B. No
Answer: B
Explanation:
Explanation
References:
https://docs.microsoft.com/en-us/office365/securitycompliance/working-with-compliance-manager
NEW QUESTION 80
You have a Microsoft 365 E5 subscription that contains the users shown in the following table.
For contoso.com, you create a group naming policy that has the following configuration.
<Department> - <Group name>
You plan to create the groups shown in the following table.
Which users can be used to create each group? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Reference:
https://office365itpros.com/2020/01/22/using-groups-admin-role/
https://docs.microsoft.com/en-us/azure/active-directory/roles/permissions-reference
NEW QUESTION 81
You have an Azure Active Directory (Azure AD) tenant named contoso.com that contains the users shown in the following table.
You register devices in contoso.com as shown in the following table.
You create app protection policies in Intune as shown in the following table.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
References:
https://docs.microsoft.com/en-us/intune/apps/app-protection-policy
NEW QUESTION 82
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some questions sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You have a Microsoft 365 subscription that contains the users shown in the following table.
You discover that all the users in the subscription can access Compliance Manager reports.
The Compliance Manager Reader role is not assigned to any users.
You need to recommend a solution to prevent a user named User5 from accessing the Compliance Manager reports.
Solution: You recommend removing User1 from the Compliance Manager Contributor role.
Does this meet the goal?
- A. Yes
- B. No
Answer: B
Explanation:
Explanation/Reference:
References:
https://docs.microsoft.com/en-us/office365/securitycompliance/working-with-compliance-manager
NEW QUESTION 83
You have a Microsoft 365 subscription.
You are creating a retention policy named Retention1 as shown in the following exhibit.
You apply Retention1 to SharePoint sites and OneDrive accounts.
Use the drop-down menus to select the answer choice that completes each statement based on the information presented in the graphic.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation
NEW QUESTION 84
Please wait while the virtual machine loads. Once loaded, you may proceed to the lab section. This may take a few minutes, and the wait time will not be deducted from your overall test time.
When the Next button is available, click it to access the lab section. In this section, you will perform a set of tasks in a live environment. While most functionality will be available to you as it would be in a live environment, some functionality (e.g., copy and paste, ability to navigate to external websites) will not be possible by design.
Scoring is based on the outcome of performing the tasks stated in the lab. In other words, it doesn't matter how you accomplish the task, if you successfully perform it, you will earn credit for that task.
Labs are not timed separately, and this exam may more than one lab that you must complete. You can use as much time as you would like to complete each lab. But, you should manage your time appropriately to ensure that you are able to complete the lab(s) and all other sections of the exam in the time provided.
Please note that once you submit your work by clicking the Next button within a lab, you will NOT be able to return to the lab.
Username and password
Use the following login credentials as needed:
To enter your username, place your cursor in the Sign in box and click on the username below.
To enter your password, place your cursor in the Enter password box and click on the password below.
Microsoft 365 Username:
admin@[email protected]
Microsoft 365 Password: &=Q8v@2qGzYz
If the Microsoft 365 portal does not load successfully in the browser, press CTRL-K to reload the portal in a new browser tab.
The following information is for technical support only:
Lab instance: 11032396
You need to create a case that prevents the members of a group named Operations from deleting email messages that contain the word IPO.
To complete this task, sign in to the Microsoft Office 365 admin center.
Answer:
Explanation:
1. Navigate to the Security & Compliance Center.
2. In the Security & Compliance Center, click eDiscovery > eDiscovery, and then click Create a case.
3. On the New Case page, give the case a name, type an optional description, and then click Save. The case name must be unique in your organization.
The new case is displayed in the list of cases on the eDiscovery page.
After you create a case, the next step is to add members to the case. The eDiscovery Manager who created the case is automatically added as a member. Members have to be assigned the appropriate eDiscovery permissions so they can access the case after you add them.
4. In the Security & Compliance Center, click eDiscovery > eDiscovery to display the list of cases in your organization.
5. Click the name of the case that you want to add members to.
The Manage this case flyout page is displayed.
6. Under Manage members, click Add to add members to the case.You can also choose to add a role group to the case. Under Manage role groups, click Add.
7. In the list of people or role groups that can be added as members of the case, click the check box next to the names of the people or role groups that you want to add.
8. After you select the people or role groups to add as members of the group, click Add.In Manage this case, click Save to save the new list of case members.
9. Click Save to save the new list of case members.
You can use an eDiscovery case to create holds to preserve content that might be relevant to the case. You can place a hold on the mailboxes and OneDrive for Business sites of people who are custodians in the case. You can also place a hold on the group mailbox, SharePoint site, and OneDrive for Business site for an Office 365 Group. Similarly, you can place a hold on the mailboxes and sites that are associated with Microsoft Teams or Yammer Groups. When you place content locations on hold, content is held until you remove the hold from the content location or until you delete the hold.
To create a hold for an eDiscovery case:
1. In the Security & Compliance Center, click eDiscovery > eDiscovery to display the list of cases in your organization.
2. Click Open next to the case that you want to create the holds in.
3. On the Home page for the case, click the Hold tab.
4. On the Hold page, click Create.
5. On the Name your hold page, give the hold a name. The name of the hold must be unique in your organization.
6. (Optional) In the Description box, add a description of the hold.
7. Click Next.
8. Choose the content locations that you want to place on hold. You can place mailboxes, sites, and public folders on hold.
a. Exchange email - Click Choose users, groups, or teams and then click Choose users, groups, or teams again.
to specify mailboxes to place on hold. Use the search box to find user mailboxes and distribution groups (to place a hold on the mailboxes of group members) to place on hold. You can also place a hold on the associated mailbox for a Microsoft Team, a Yammer Group, or an Office 365 Group. Select the user, group, team check box, click Choose, and then click Done.
a. In the box under Keywords, type a search query in the box so that only the content that meets the search criteria is placed on hold. You can specify keywords, message properties, or document properties, such as file names. You can also use more complex queries that use a Boolean operator, such as AND, OR, or NOT. If you leave the keyword box empty, then all content located in the specified content locations will be placed on hold.
b. Click Add conditions to add one or more conditions to narrow the search query for the hold. Each condition adds a clause to the KQL search query that is created and run when you create the hold. For example, you can specify a date range so that email or site documents that were created within the date ranged are placed on hold. A condition is logically connected to the keyword query (specified in the keyword box) by the AND operator. That means that items have to satisfy both the keyword query and the condition to be placed on hold.
9. After configuring a query-based hold, click Next.
10. Review your settings, and then click Create this hold.
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/ediscovery-cases?view=o365-worldwide
NEW QUESTION 85
You need to meet the technical requirements for User9. What should you do?
- A. Assignthe Security administrator role to User9
- B. Assign the Privileged administrator role to User9 and configure a mobile phone number for User9
- C. Assign the Compliance administrator role to User9 and configure a mobile phone number for User9
- D. Assign the Global administrator role to User9
Answer: B
Explanation:
Explanation
https://docs.microsoft.com/en-us/azure/active-directory/privileged-identity-management/pim-how-to-give-acces
NEW QUESTION 86
You have a Microsoft 365 subscription.
A security manager receives an email message every time a data loss prevention (DLP) policy match occurs.
You need to limit alert notifications to actionable DLP events.
What should you do?
- A. From the Security & Compliance admin center, modify the matched activities threshold of an alert policy.
- B. From the Security & Compliance admin center, modify the User overrides settings of a DLP policy.
- C. From the Cloud App Security admin center, apply a filter to the alerts.
- D. From the Security & Compliance admin center, modify the Policy Tips of a DLP policy.
Answer: A
Explanation:
Explanation
References:
https://docs.microsoft.com/en-us/office365/securitycompliance/alert-policies
NEW QUESTION 87
How should you configure Group3? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
NEW QUESTION 88
You have a Microsoft 365 subscription.
Some users access Microsoft SharePoint Online from unmanaged devices.
You need to prevent the users from downloading, printing, and syncing files.
What should you do?
- A. From the Microsoft Azure portal, create an Azure Active Directory (Azure AD) Identity Protection sign-in risk policy
- B. From the SharePoint admin center, configure the Access control settings
- C. Run the Set-SPODataConnectionSettingcmdlet and specify the AssignmentCollection parameter
- D. From the Microsoft Azure portal, create an Azure Active Directory (Azure AD) conditional access policy
Answer: B
Explanation:
Explanation/Reference:
https://docs.microsoft.com/en-us/sharepoint/control-access-from-unmanaged-devices
NEW QUESTION 89
Please wait while the virtual machine loads. Once loaded, you may proceed to the lab section. This may take a few minutes, and the wait time will not be deducted from your overall test time.
When the Next button is available, click it to access the lab section. In this section, you will perform a set of tasks in a live environment. While most functionality will be available to you as it would be in a live environment, some functionality (e.g., copy and paste, ability to navigate to external websites) will not be possible by design.
Scoring is based on the outcome of performing the tasks stated in the lab. In other words, it doesn't matter how you accomplish the task, if you successfully perform it, you will earn credit for that task.
Labs are not timed separately, and this exam may more than one lab that you must complete. You can use as much time as you would like to complete each lab. But, you should manage your time appropriately to ensure that you are able to complete the lab(s) and all other sections of the exam in the time provided.
Please note that once you submit your work by clicking the Next button within a lab, you will NOT be able to return to the lab.
Username and password
Use the following login credentials as needed:
To enter your username, place your cursor in the Sign in box and click on the username below.
To enter your password, place your cursor in the Enter password box and click on the password below.
Microsoft 365 Username:
admin@[email protected]
Microsoft 365 Password: #HSP.ug?$p6un
If the Microsoft 365 portal does not load successfully in the browser, press CTRL-K to reload the portal in a new browser tab.
The following information is for technical support only:
Lab instance: 11122308


You need to create an Azure Information Protection label to meet the following requirements:
Content must expire after 21 days.
Offline access must be allowed for 21 days only.
Documents must be protected by using a cloud key.
Authenticated users must be able to view content only.
To complete this task, sign in to the Microsoft 365 admin center.
Answer:
Explanation:
1. If you haven't already done so, open a new browser window and sign in to the Azure portal. Then navigate to the Azure Information Protection pane.
For example, in the search box for resources, services, and docs: Start typing Information and select Azure Information Protection.
2. From the Classifications > Labels menu option: On the Azure Information Protection - Labels pane, select the label you want to change.
On the Label pane, locate Set permissions for documents and emails containing this label, and select Protect.
3. Select Protection.
4. On the Protection pane, select Azure (cloud key).
5. Select Set permissions to define new protection settings in this portal.
6. If you selected Set permissions for Azure (cloud key), this option lets you select users and usage rights.
To specify the users that you want to be able to open protected documents and emails, select Add permissions. Then on the Add permissions pane, select the first set of users and groups who will have rights to use the content that will be protected by the selected label:
Choose Select from the list where you can then add all users from your organization by selecting Add <organization name> - All members. This setting excludes guest accounts. Or, you can select Add any authenticated users, or browse the directory.
When you choose all members or browse the directory, the users or groups must have an email address. In a production environment, users and groups nearly always have an email address, but in a simple testing environment, you might need to add email addresses to user accounts or groups.
Change the File Content Expiration setting to 21 days.
Change the Allow offline access setting to 21 days.
When you have finished configuring the permissions and settings, click OK.
This grouping of settings creates a custom template for the Azure Rights Management service. These templates can be used with applications and services that integrate with Azure Rights Management.
7. Click OK to close the Protection pane and see your choice of User defined or your chosen template display for the Protection option in the Label pane.
8. On the Label pane, click Save.
9. On the Azure Information Protection pane, use the PROTECTION column to confirm that your label now displays the protection setting that you want:
A check mark if you have configured protection.
An x mark to denote cancellation if you have configured a label to remove protection.
A blank field when protection is not set.
When you clicked Save, your changes are automatically available to users and services. There's no longer a separate publish option.
Reference:
https://docs.microsoft.com/en-us/azure/information-protection/configure-policy-protection
NEW QUESTION 90
You have a Microsoft 365 subscription.
You are creating a retention policy named Retention1 as shown in the following exhibit.
You apply Retention1 to SharePoint sites and OneDrive accounts.
Use the drop-down menus to select the answer choice that completes each statement based on the information presented in the graphic.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
NEW QUESTION 91
You have a Microsoft 365 E5 subscription
You need to use Microsoft Cloud App Security to identify documents stored in Microsoft SharePomt Online that contain proprietary information.
What should you create in Cloud App Security?
- A. a data source and an app discovery policy
- B. a data source and a file policy
- C. an app connector and a We policy
- D. an app connector and an app discovery policy
Answer: A
NEW QUESTION 92
Please wait while the virtual machine loads. Once loaded, you may proceed to the lab section. This may take a few minutes, and the wait time will not be deducted from your overall test time.
When the Next button is available, click it to access the lab section. In this section, you will perform a set of tasks in a live environment. While most functionality will be available to you as it would be in a live environment, some functionality (e.g., copy and paste, ability to navigate to external websites) will not be possible by design.
Scoring is based on the outcome of performing the tasks stated in the lab. In other words, it doesn't matter how you accomplish the task, if you successfully perform it, you will earn credit for that task.
Labs are not timed separately, and this exam may more than one lab that you must complete. You can use as much time as you would like to complete each lab. But, you should manage your time appropriately to ensure that you are able to complete the lab(s) and all other sections of the exam in the time provided.
Please note that once you submit your work by clicking the Next button within a lab, you will NOT be able to return to the lab.
Username and password
Use the following login credentials as needed:
To enter your username, place your cursor in the Sign in box and click on the username below.
To enter your password, place your cursor in the Enter password box and click on the password below.
Microsoft 365 Username:
admin@[email protected]
Microsoft 365 Password: &=Q8v@2qGzYz
If the Microsoft 365 portal does not load successfully in the browser, press CTRL-K to reload the portal in a new browser tab.
The following information is for technical support only:
Lab instance: 11032396
You need to ensure that each user can join up to five devices to Azure Active Directory (Azure AD).
To complete this task, sign in to the Microsoft Office 365 admin center.
Answer:
Explanation:
See explanation below.
* After signing into the Microsoft 365 admin center, click Admin centers > Azure Active Directory >
* Devices.
* Navigate to Device Settings.
* Set the Users may join devices to Azure AD setting to All.
* Set the Additional local administrators on Azure AD joined devices setting to None.
* Set the Users may register their devices with Azure AD setting to All.
* Leave the Require Multi-Factor Auth to join devices setting on it default setting.
* Set the Maximum number of devices setting to 5.
* Set the Users may sync settings and app data across devices setting to All.
* Click the Save button at the top left of the screen.
Reference:
https://docs.microsoft.com/en-us/azure/active-directory/devices/device-management-azure-portal
https://docs.microsoft.com/en-us/microsoft-365/compliance/use-your-free-azure-ad-subscription-in-office-365?v
NEW QUESTION 93
You are evaluating which devices are compliant in Intune.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation
NEW QUESTION 94
Which policies apply to which devices? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
NEW QUESTION 95
You have a Microsoft 365 E5 subscription that contains an Azure Active Directory (Azure AD) tenant named contoso.com.
Azure AD Identity Protection alerts for contoso.com are configured as shown in the following exhibit.
A user named User1 is configured to receive alerts from Azure AD Identity Protection.
You create users in contoso.com as shown in the following table.
The users perform the sign-ins shown in the following table.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Reference:
https://docs.microsoft.com/en-us/azure/active-directory/identity-protection/overview-identity-protection
https://docs.microsoft.com/en-us/azure/active-directory/identity-protection/howto-identity-protection-configure-risk-policies
NEW QUESTION 96
......
What Are the Career Opportunities and Their Salary Scale?
A professional who has succeeded in MS-500 exam and has earned the Microsoft 365 Certified: Security Administrator Associate certificate can secure well paying jobs that require knowledge of cloud technologies like those services offered by Microsoft 365 managed by Azure.
MS-500 Premium Exam Engine - Download Free PDF Questions: https://www.actualvce.com/Microsoft/MS-500-valid-vce-dumps.html
Instant Download MS-500 Free Updated Test Dumps: https://drive.google.com/open?id=199S5O6s5qARpzQmApQTUielj6In1CbIk